API Keys and Authorized Apps
API keys and authorized apps control how outside systems access a workspace. This guide explains when to use each credential type, how to create credentials safely, and when to revoke access.
Create an API Key
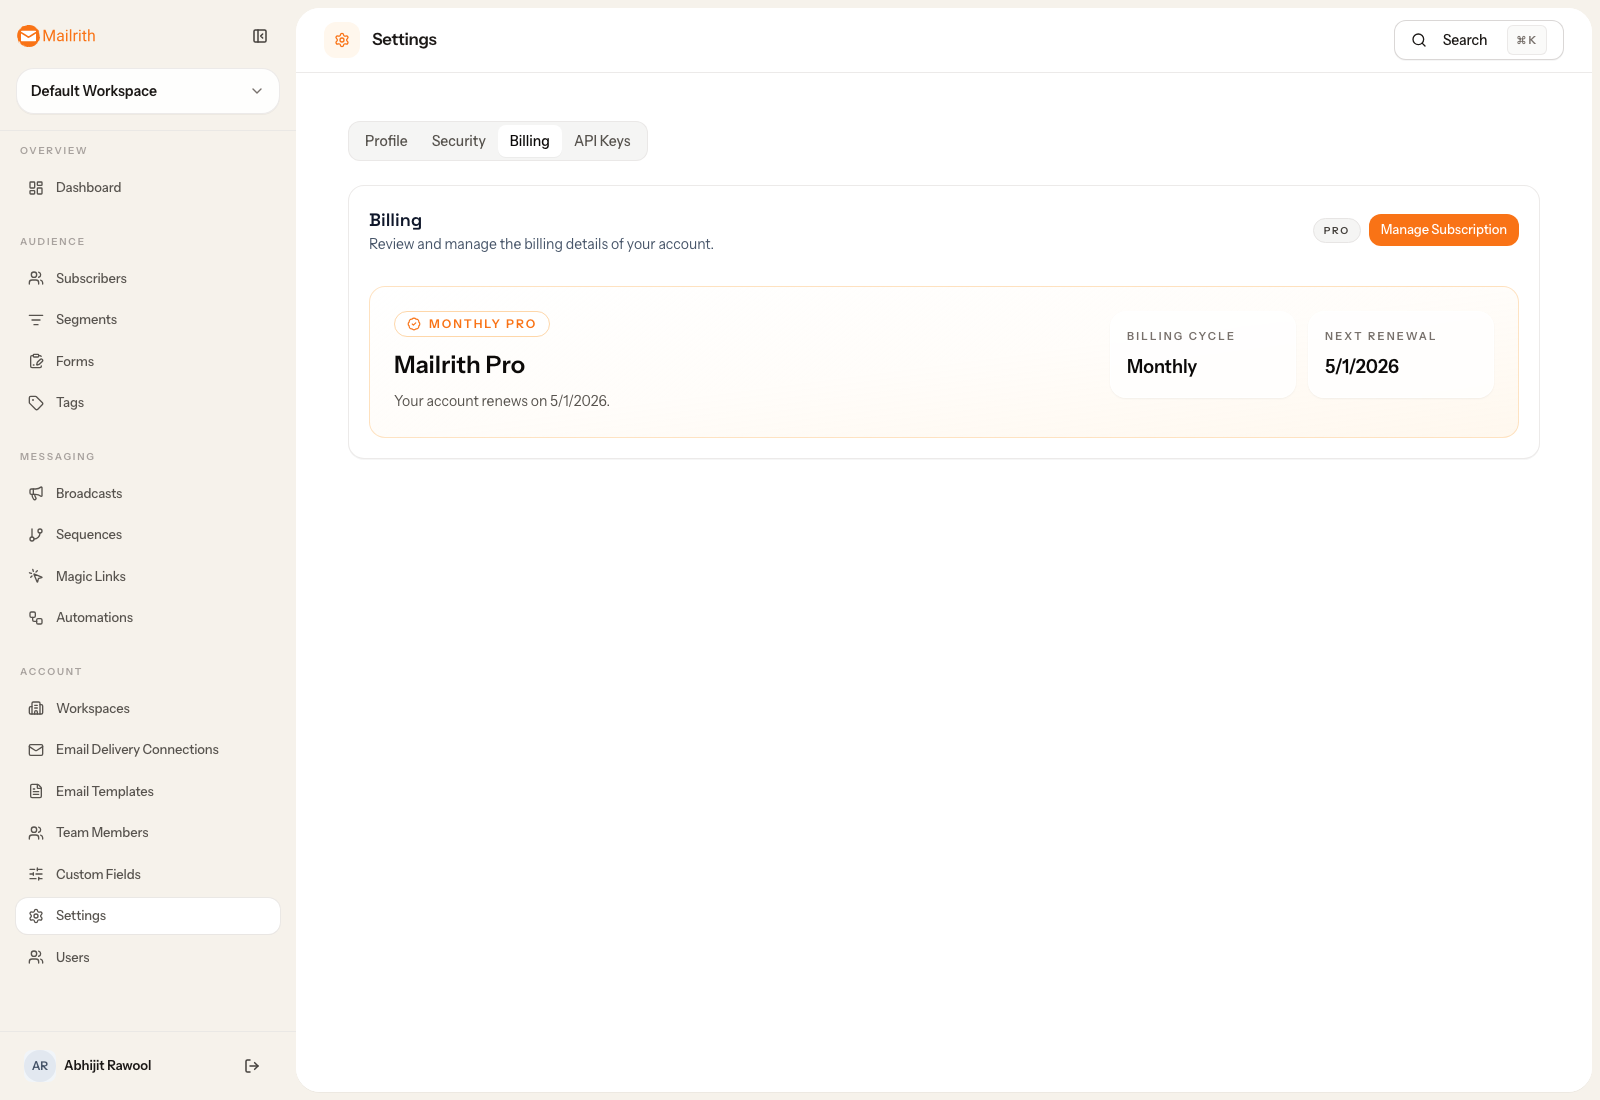
Workspace owners and teammates with Manage API Keys create API keys from Settings on the API Keys tab. Teammates with View API Keys can review the list but cannot generate, rotate, or revoke keys. Create a separate key for each integration so you can rotate or revoke one integration without affecting the others. For example, use one key for your website sign-up form, another key for a CRM sync, and another key for an imported subscriber data script. If you are building the integration yourself, create the key first, and then follow the Developer Quickstart.
- Use the workspace selector in the left sidebar to choose any workspace owned by the account whose API keys you want to manage. The API Keys tab appears when you have API key access in at least one workspace owned by that account.
- Click Settings in the left sidebar.
- Click the API Keys tab.
- Wait for the API key list to load. If Mailrith cannot load it, click Try Again. Key-changing actions remain unavailable until the list loads successfully.
- Click Generate API Key.
- In the Generate API Key drawer, choose the Workspace that the integration needs to access.
- Enter a Name that identifies the system that will use the key.
- Choose Work Profile. Full Email Marketing Access is the default for a general-purpose agent. Choose Reporting, Subscriber Management, Content And Capture, Broadcasts, Sequences, Automations, Subscriber Import And Export, Email Delivery Setup, or Outbound Webhooks when the integration has a narrower job. Choose Custom Permissions when no Work Profile fits.
- If you choose Custom Permissions, select only the actions that the integration must perform. Read each description before selecting a permission.
- Choose Expiration. Select an expiration date for a temporary key. Select Never expires only for long-running systems that your team actively owns.
- Click Generate.
- Keep the drawer open while Mailrith creates the key.
- In the Save Your API Key dialog, copy the full key immediately. Mailrith shows the full key only once.
After you close the key dialog, Mailrith keeps enough information to identify the key, but Mailrith does not show the full secret again. If you lose the full key, rotate the key or create a new key, and then update the integration with the new secret.
Rotate or Revoke API Access
Rotating a key replaces the old key with an active key that has a new secret value. Revoking a key disables access so the key can no longer be used. Revoked and replaced keys disappear from the API Keys list.
- Rotate a key when the system still needs access but the secret may have been seen by the wrong person, stored in the wrong place, or used for too long.
- Revoke a key when the integration is no longer used, a vendor relationship has ended, or you want access to stop immediately.
- After a key is revoked, create a new key if the integration needs access again.
Before you rotate a key, confirm that the person responsible for the integration is ready to update the stored secret in the connected system. Rotation is successful only after the connected system uses the new key. If the integration keeps using the old key after rotation, the integration will stop working. If that person should no longer have workspace access, remove or change their access through Team Members.
- Use the workspace selector in the left sidebar to choose any workspace owned by the account whose API keys you want to review.
- Click Settings in the left sidebar and open the API Keys tab.
- Use Search API keys to find the key by name, owner, workspace, or purpose.
- Click Rotate when the integration should keep working with a new secret value.
- Keep the dialog open while Mailrith rotates the key.
- Copy the replacement key from the dialog, update the connected system with the new key, and confirm the connected system works before you consider the rotation complete.
- Click Revoke when the integration should stop working immediately.
- Keep the dialog open until Mailrith confirms that the key was revoked.
- After Mailrith confirms the change, the revoked key disappears from the list.
Credential Safety Checklist
- Name each key after the system that uses it, not after the person who creates it.
- Store full API key values in a password manager, secret manager, or server environment variable. Do not paste API key values into shared documents or chat channels.
- Use Full Email Marketing Access for a general-purpose agent. Give a purpose-built integration a focused Work Profile or custom permission set that matches its narrower job.
- Review keys and authorized apps whenever a contractor leaves, an agency handoff occurs, or a connected tool is retired.
- Revoke any credential or authorized app you do not recognize. Create a new credential only if a real integration stops working and you can identify who owns the integration.